StrikeFirst.AI is the attack console for cyber operators. Deterministic playbooks
discover and test the attack surface inside the scope you set. A human approves
every step that touches a target, and every action lands in an append-only audit
trail: rails built for agentic AI.
probed, in scopenew discoveryrecorded, never touched
12step External VA playbook, from seed domain to scored findings
10tool integrations on a modular core, compatible with tools like OpenVAS
100%of actions audited: pre, post, error and approval
1-clickPDF and XLSX deliverables plus a SOC activity timeline
Platform
Automation you can defend in the debrief.
Operators need speed without surprises. StrikeFirst.AI makes every run repeatable,
reviewable and provable, from the first DNS lookup to the final report.
Deterministic playbooks
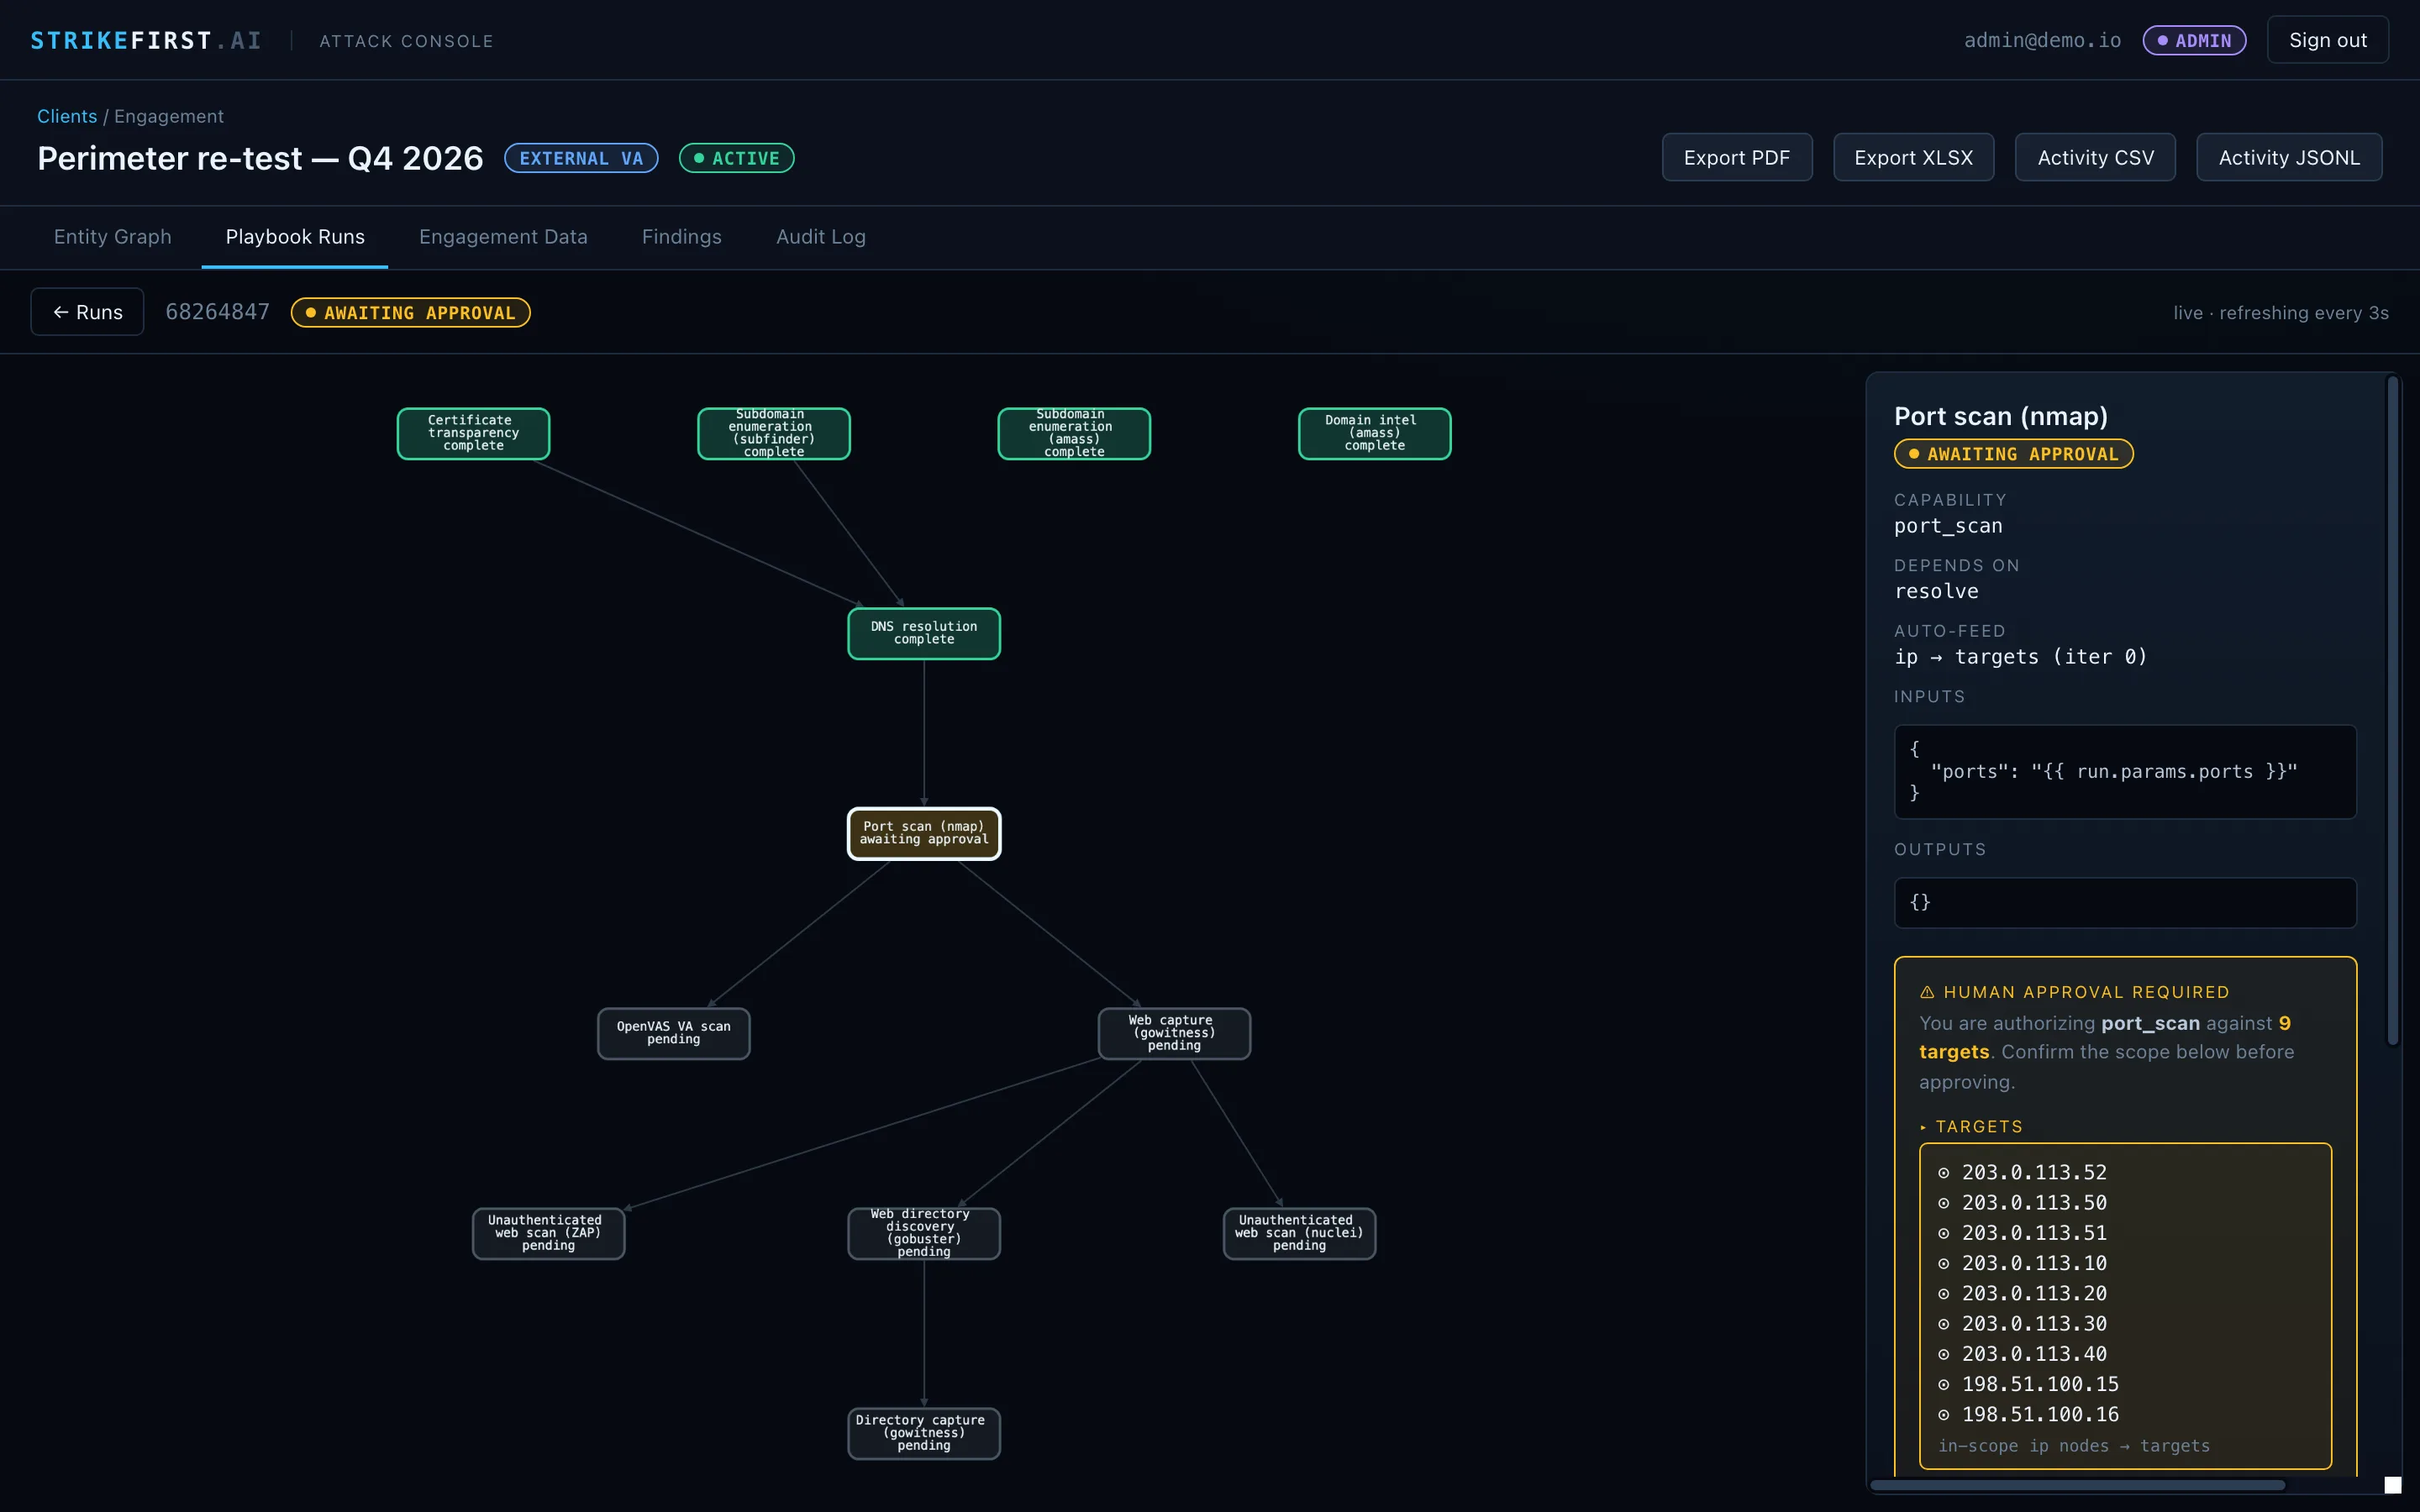
Engagements run as DAG playbooks of capabilities, not ad-hoc scripts. Discovery is
recursive, so every new in-scope host is enumerated, resolved, scanned and assessed.
It's also bounded, so the same seed produces the same run, every time.
Human in the loop
Target-touching steps stop at approval gates. Operators see the exact resolved
targets before anything runs and can edit the inputs. Every decision is recorded
with the approver and their notes.
Planned for V1.5
Agentic AI on rails
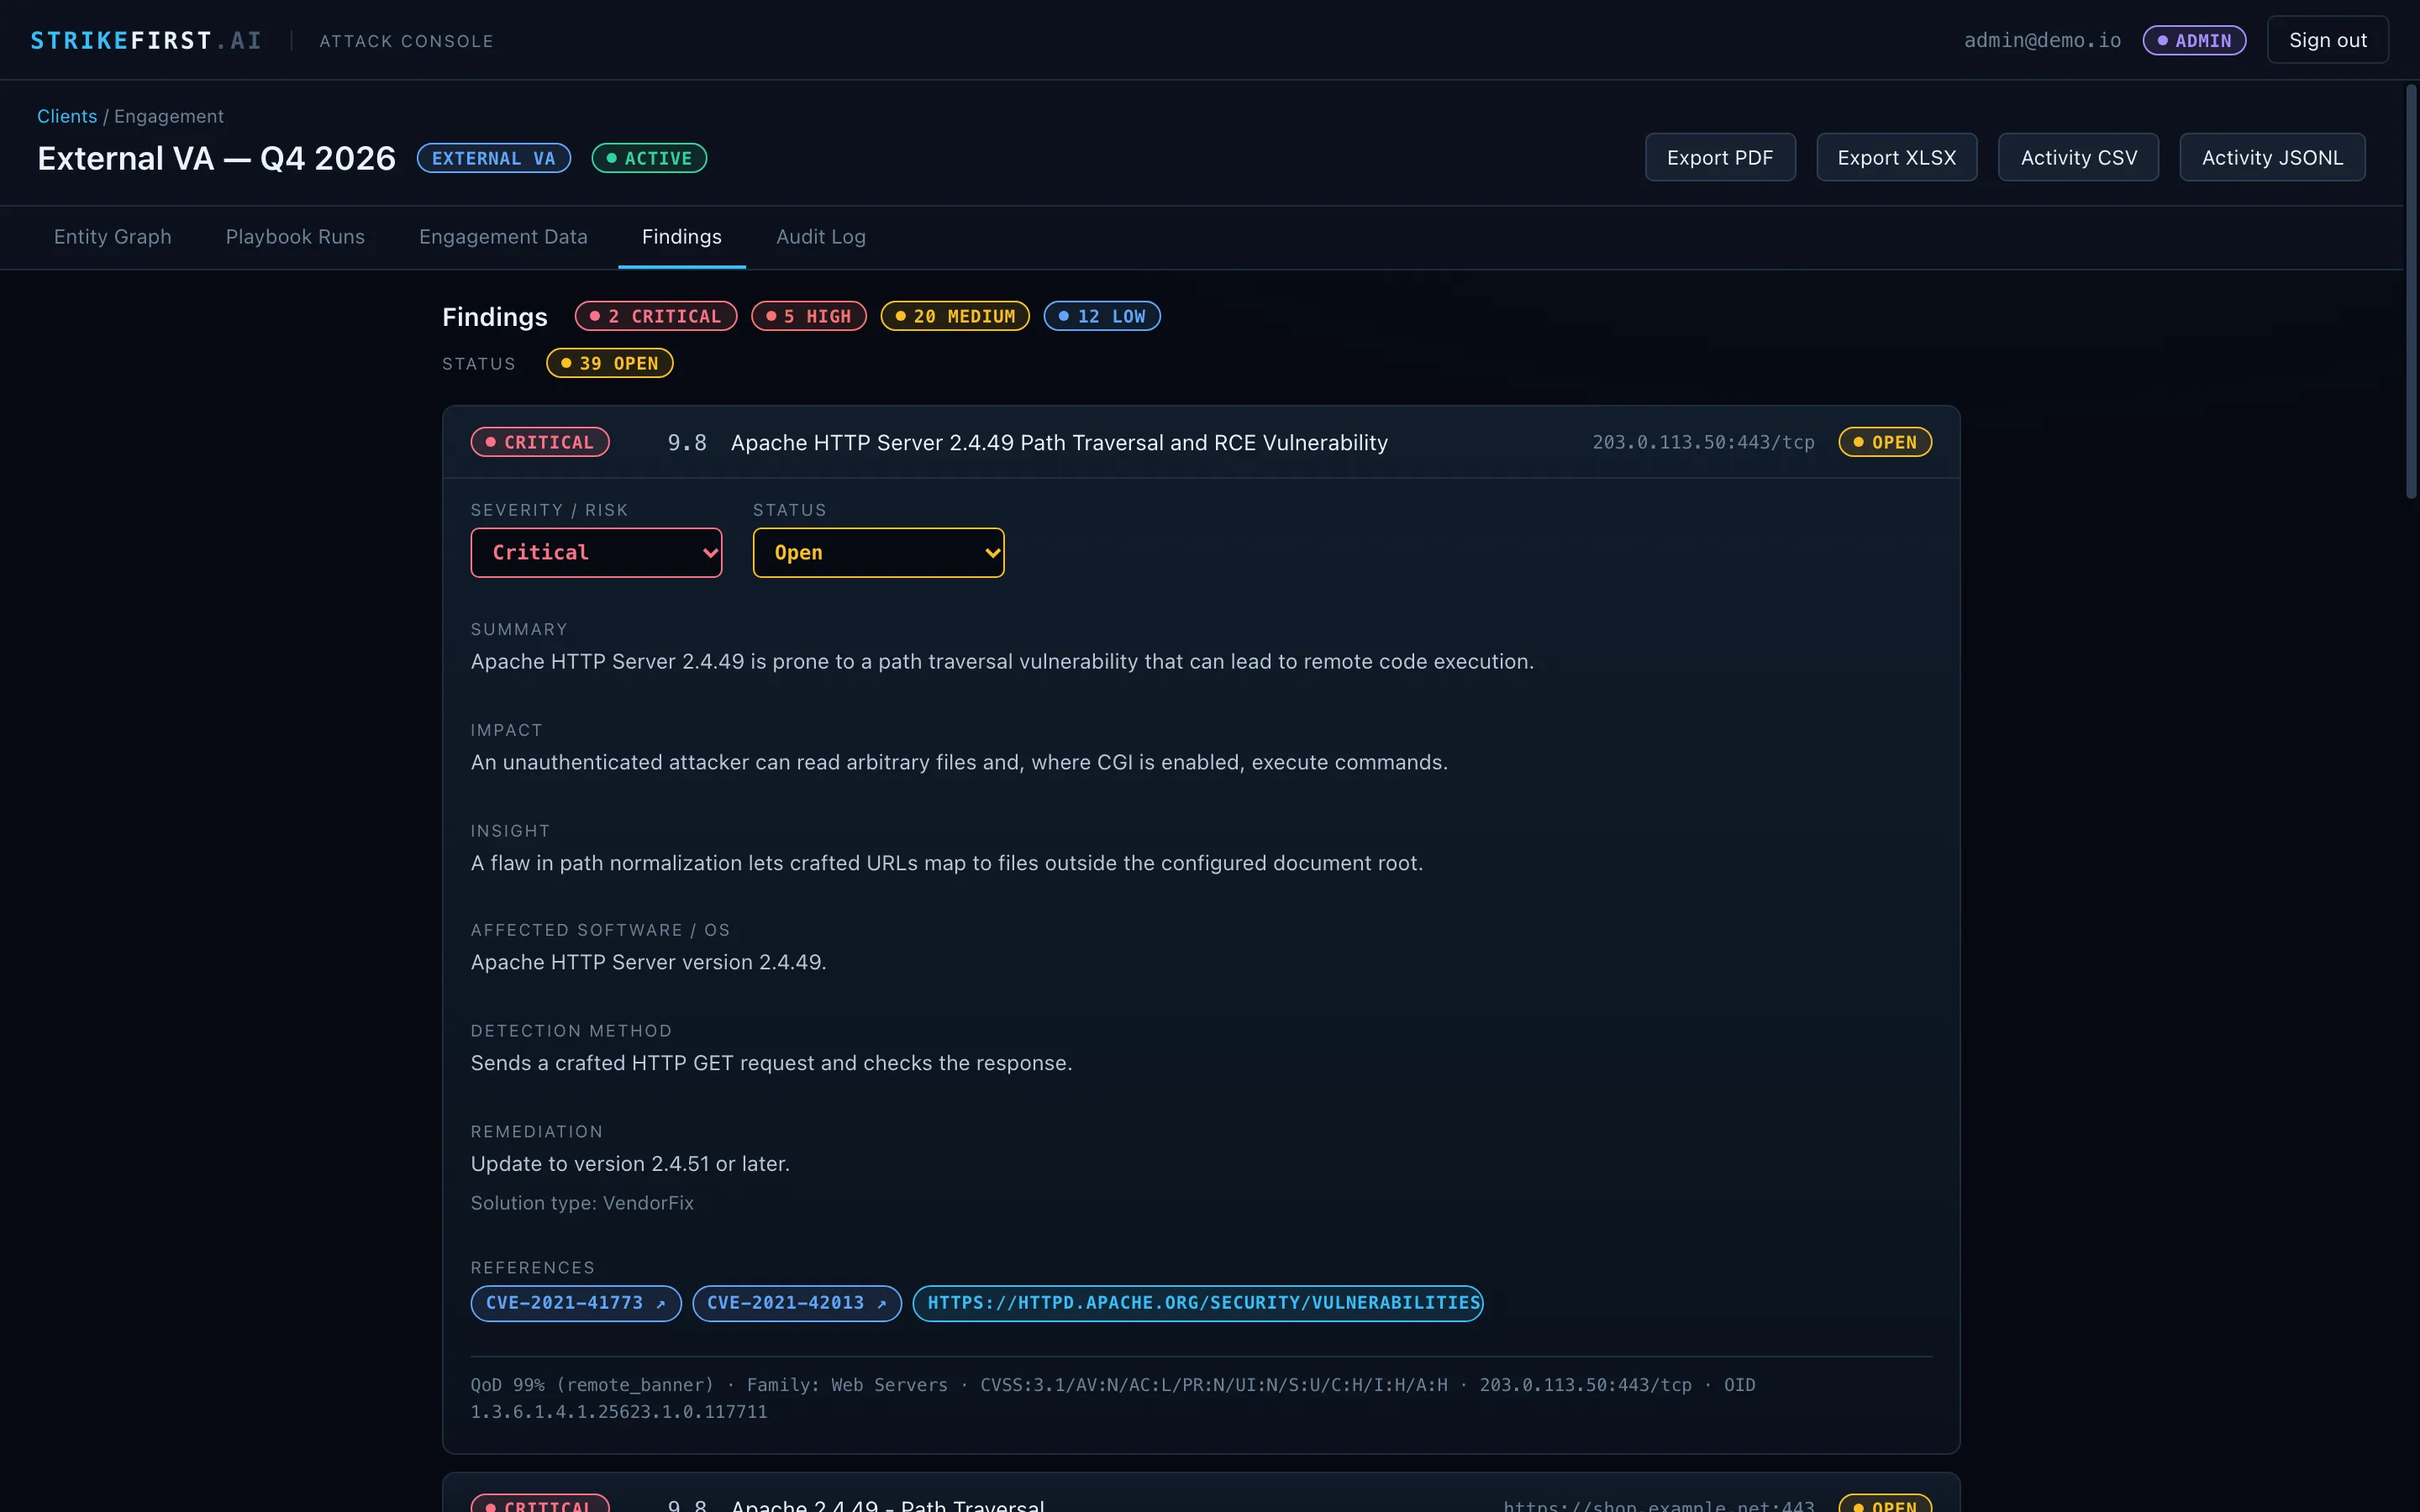
Post-run AI analysis turns raw tool output into explained, prioritized findings
and report-ready narrative. PHIL, our pseudo-human in the loop, brings agentic
automation to the playbook's decision points. Every decision, human or PHIL, goes
through the same scope enforcement and audit trail.
How it works
From seed domain to signed-off report.
One playbook, five stages, and a human decision at the moment it matters.
01
Scope
Domains, CIDRs and exclusions, tied to the engagement's authorization.
02
Discover
Passive OSINT and DNS discovery map the surface recursively.
03
Approve
The run pauses. An operator confirms the resolved targets.
Awaiting approval
04
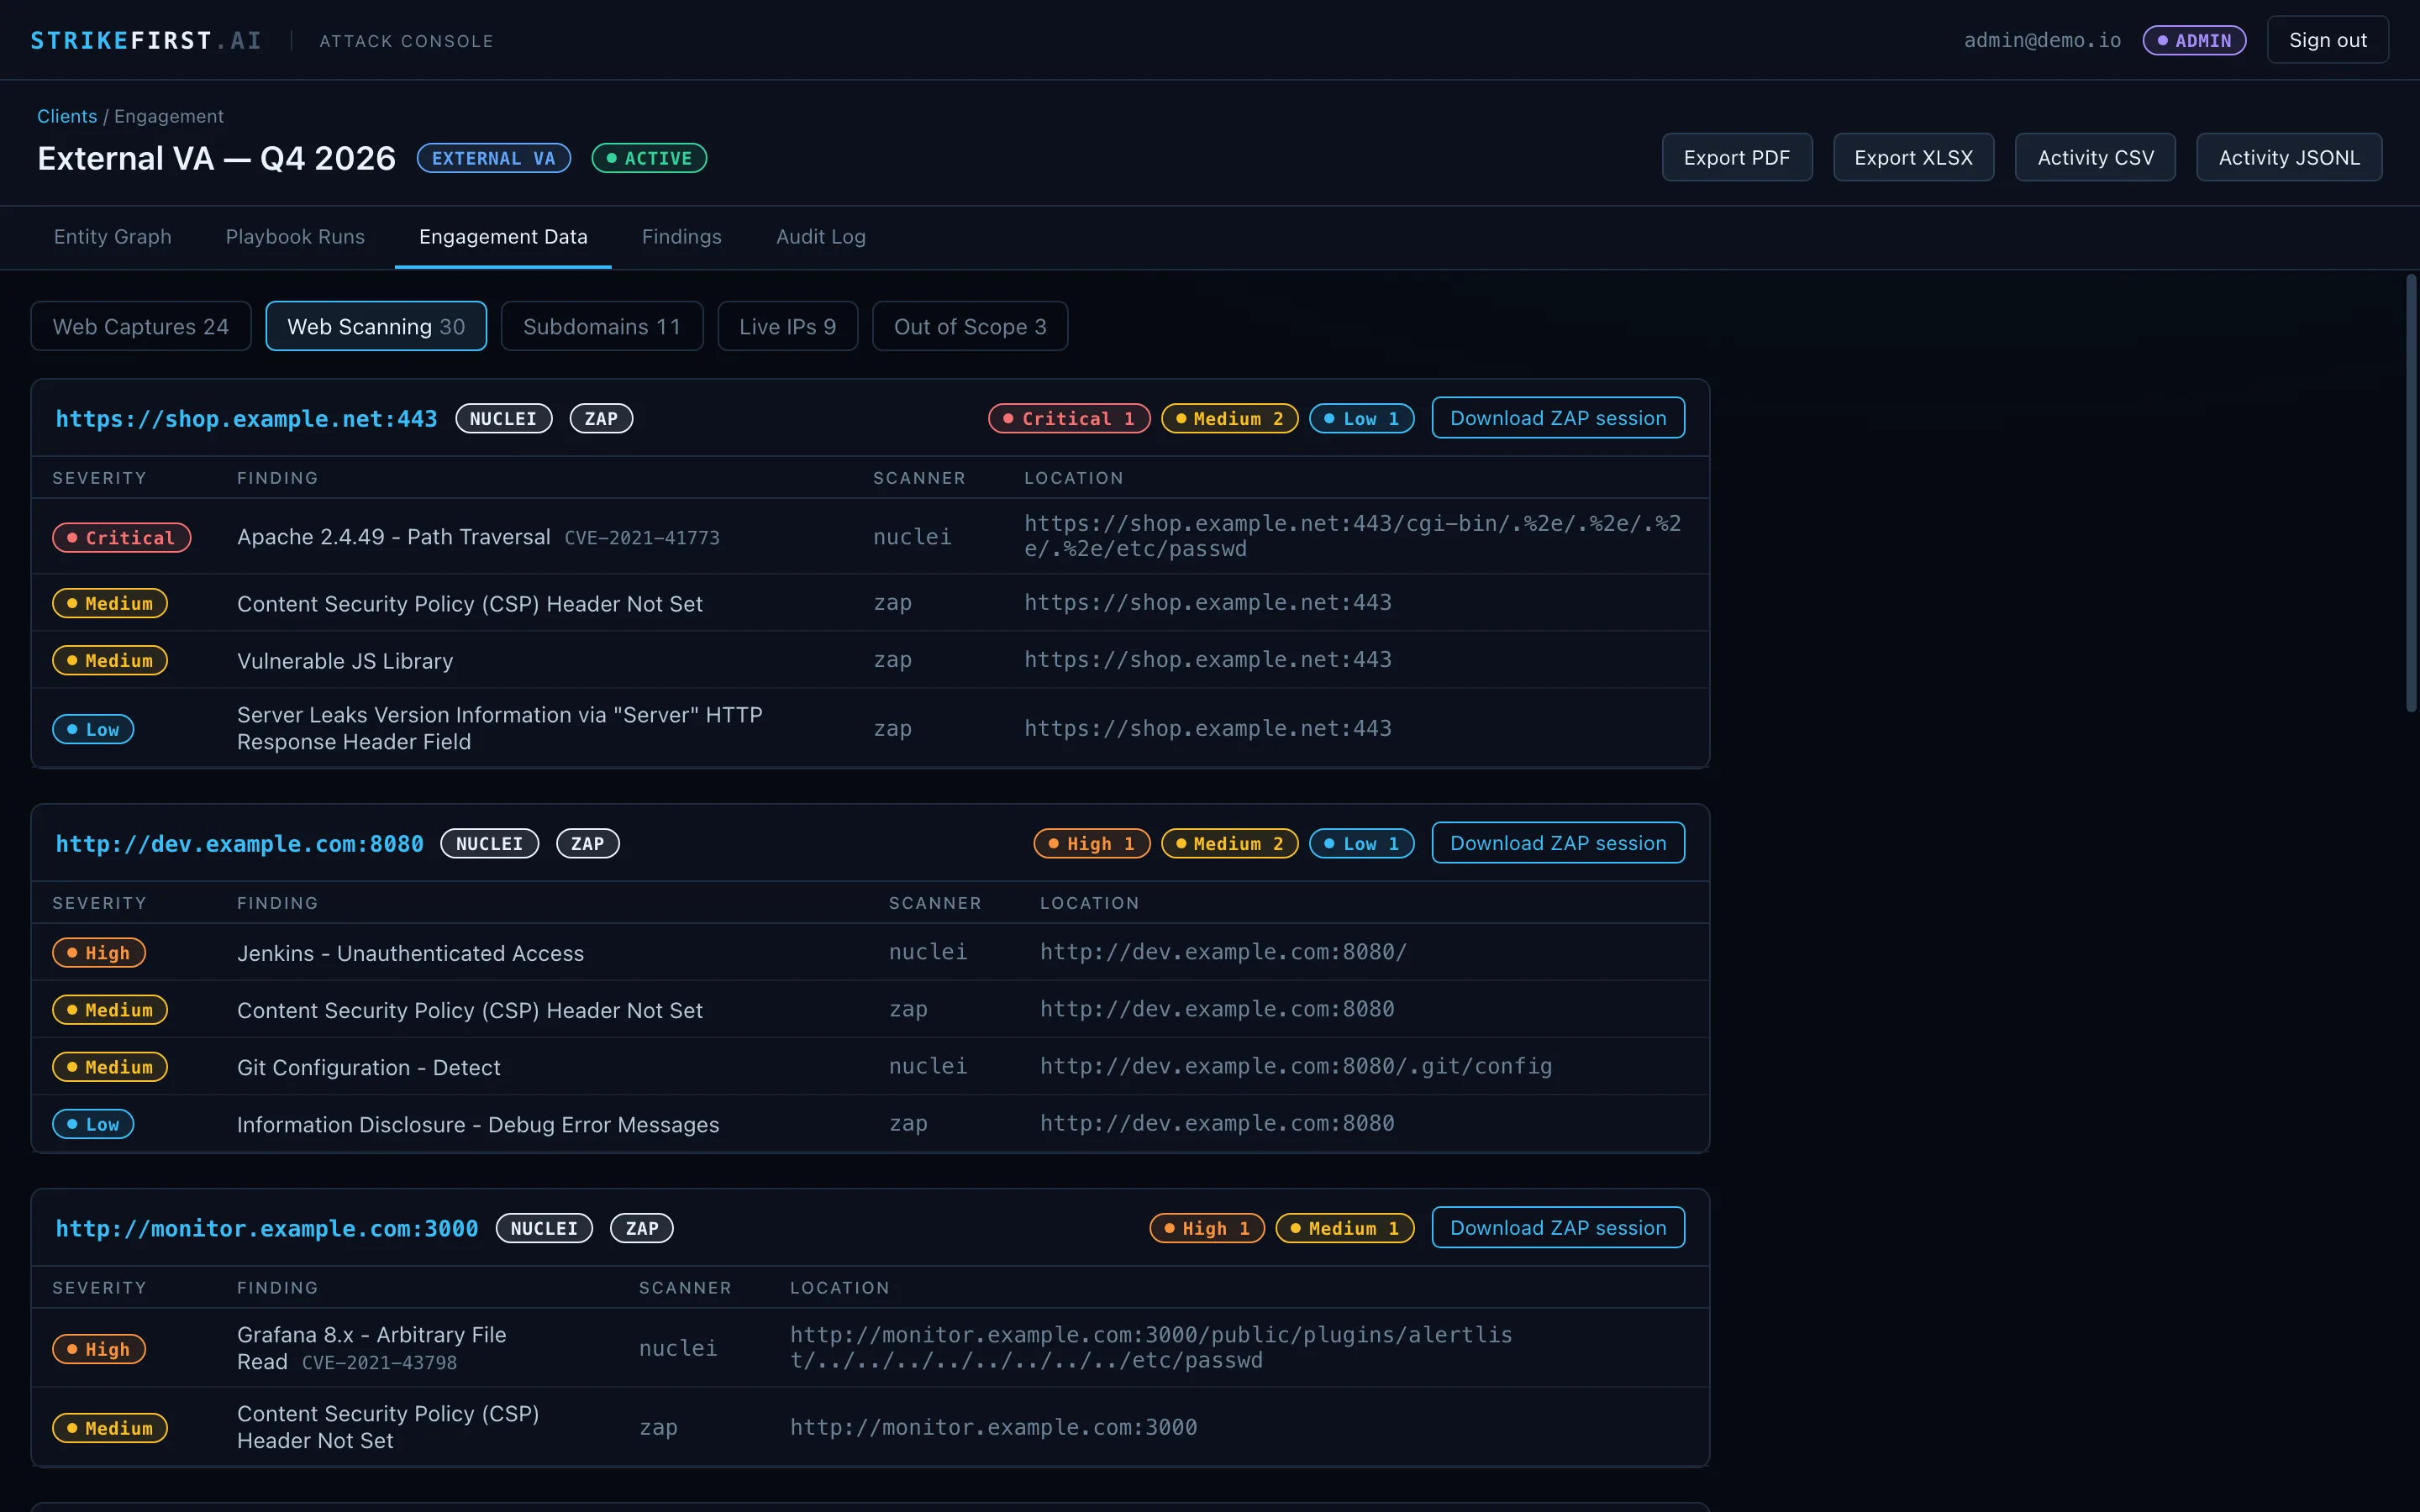
Assess
Port, vulnerability and web scanners test only what's in scope.
05
Report
PDF and XLSX deliverables, plus a timeline for the client's SOC.
Product
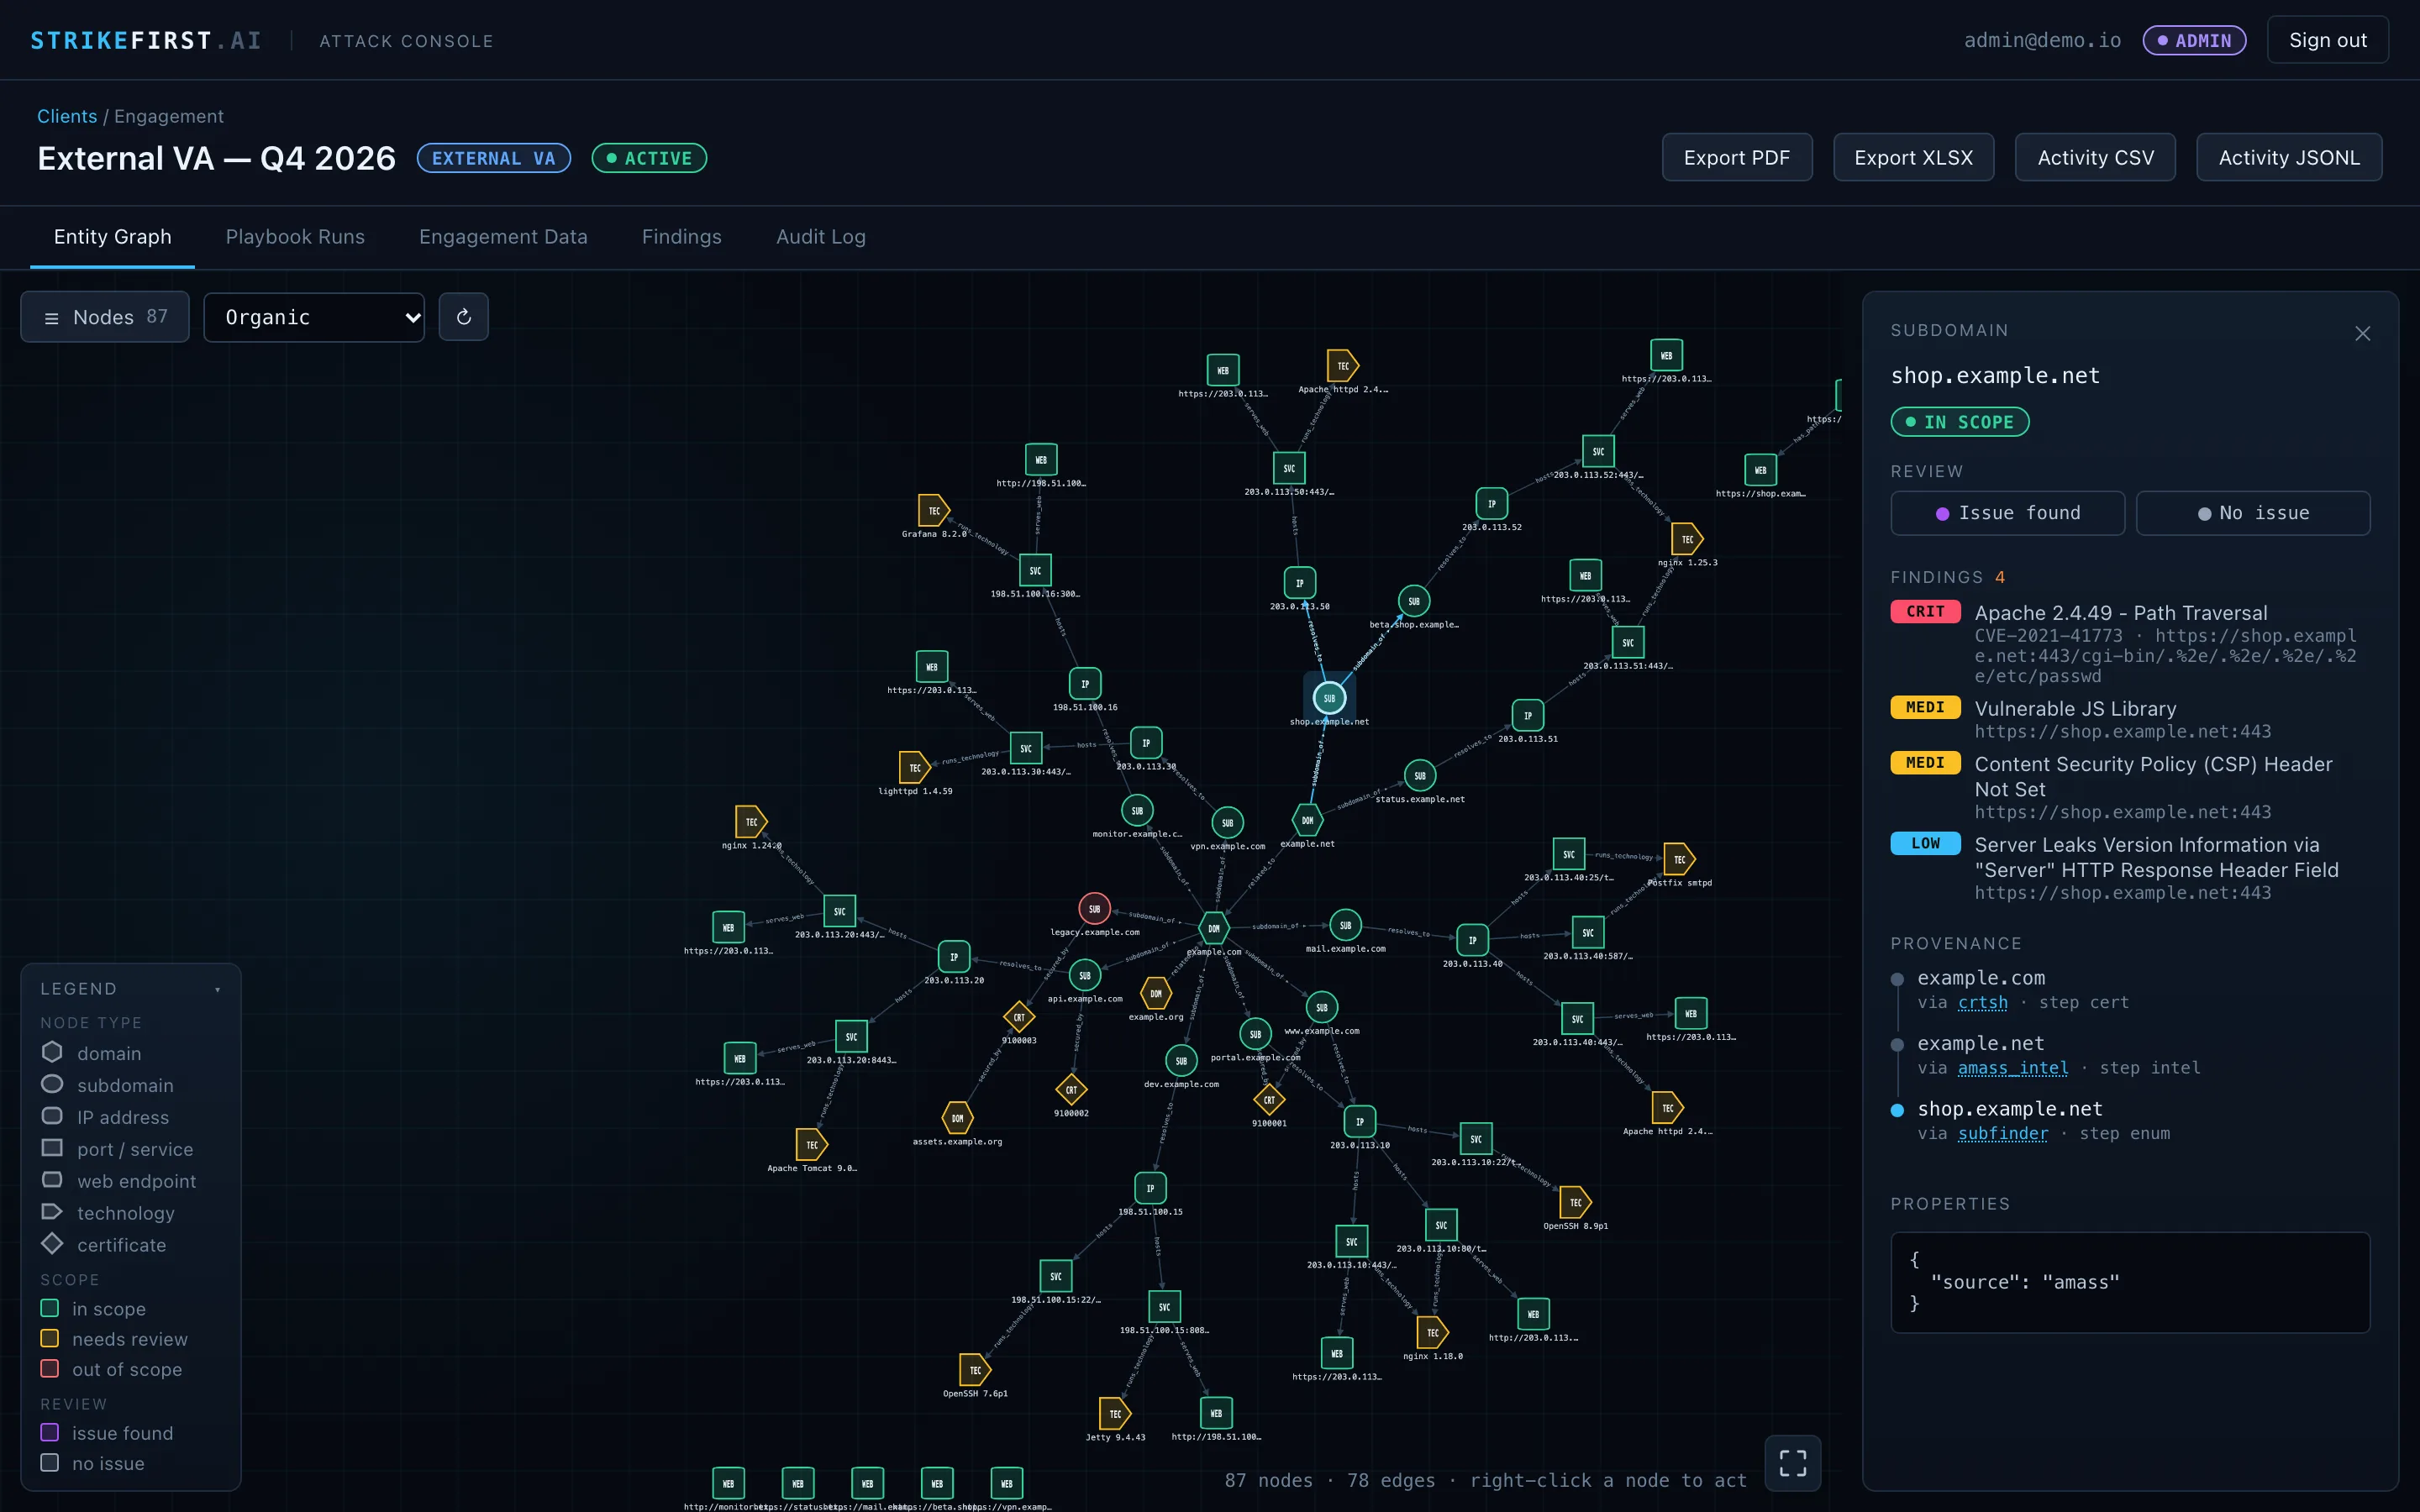
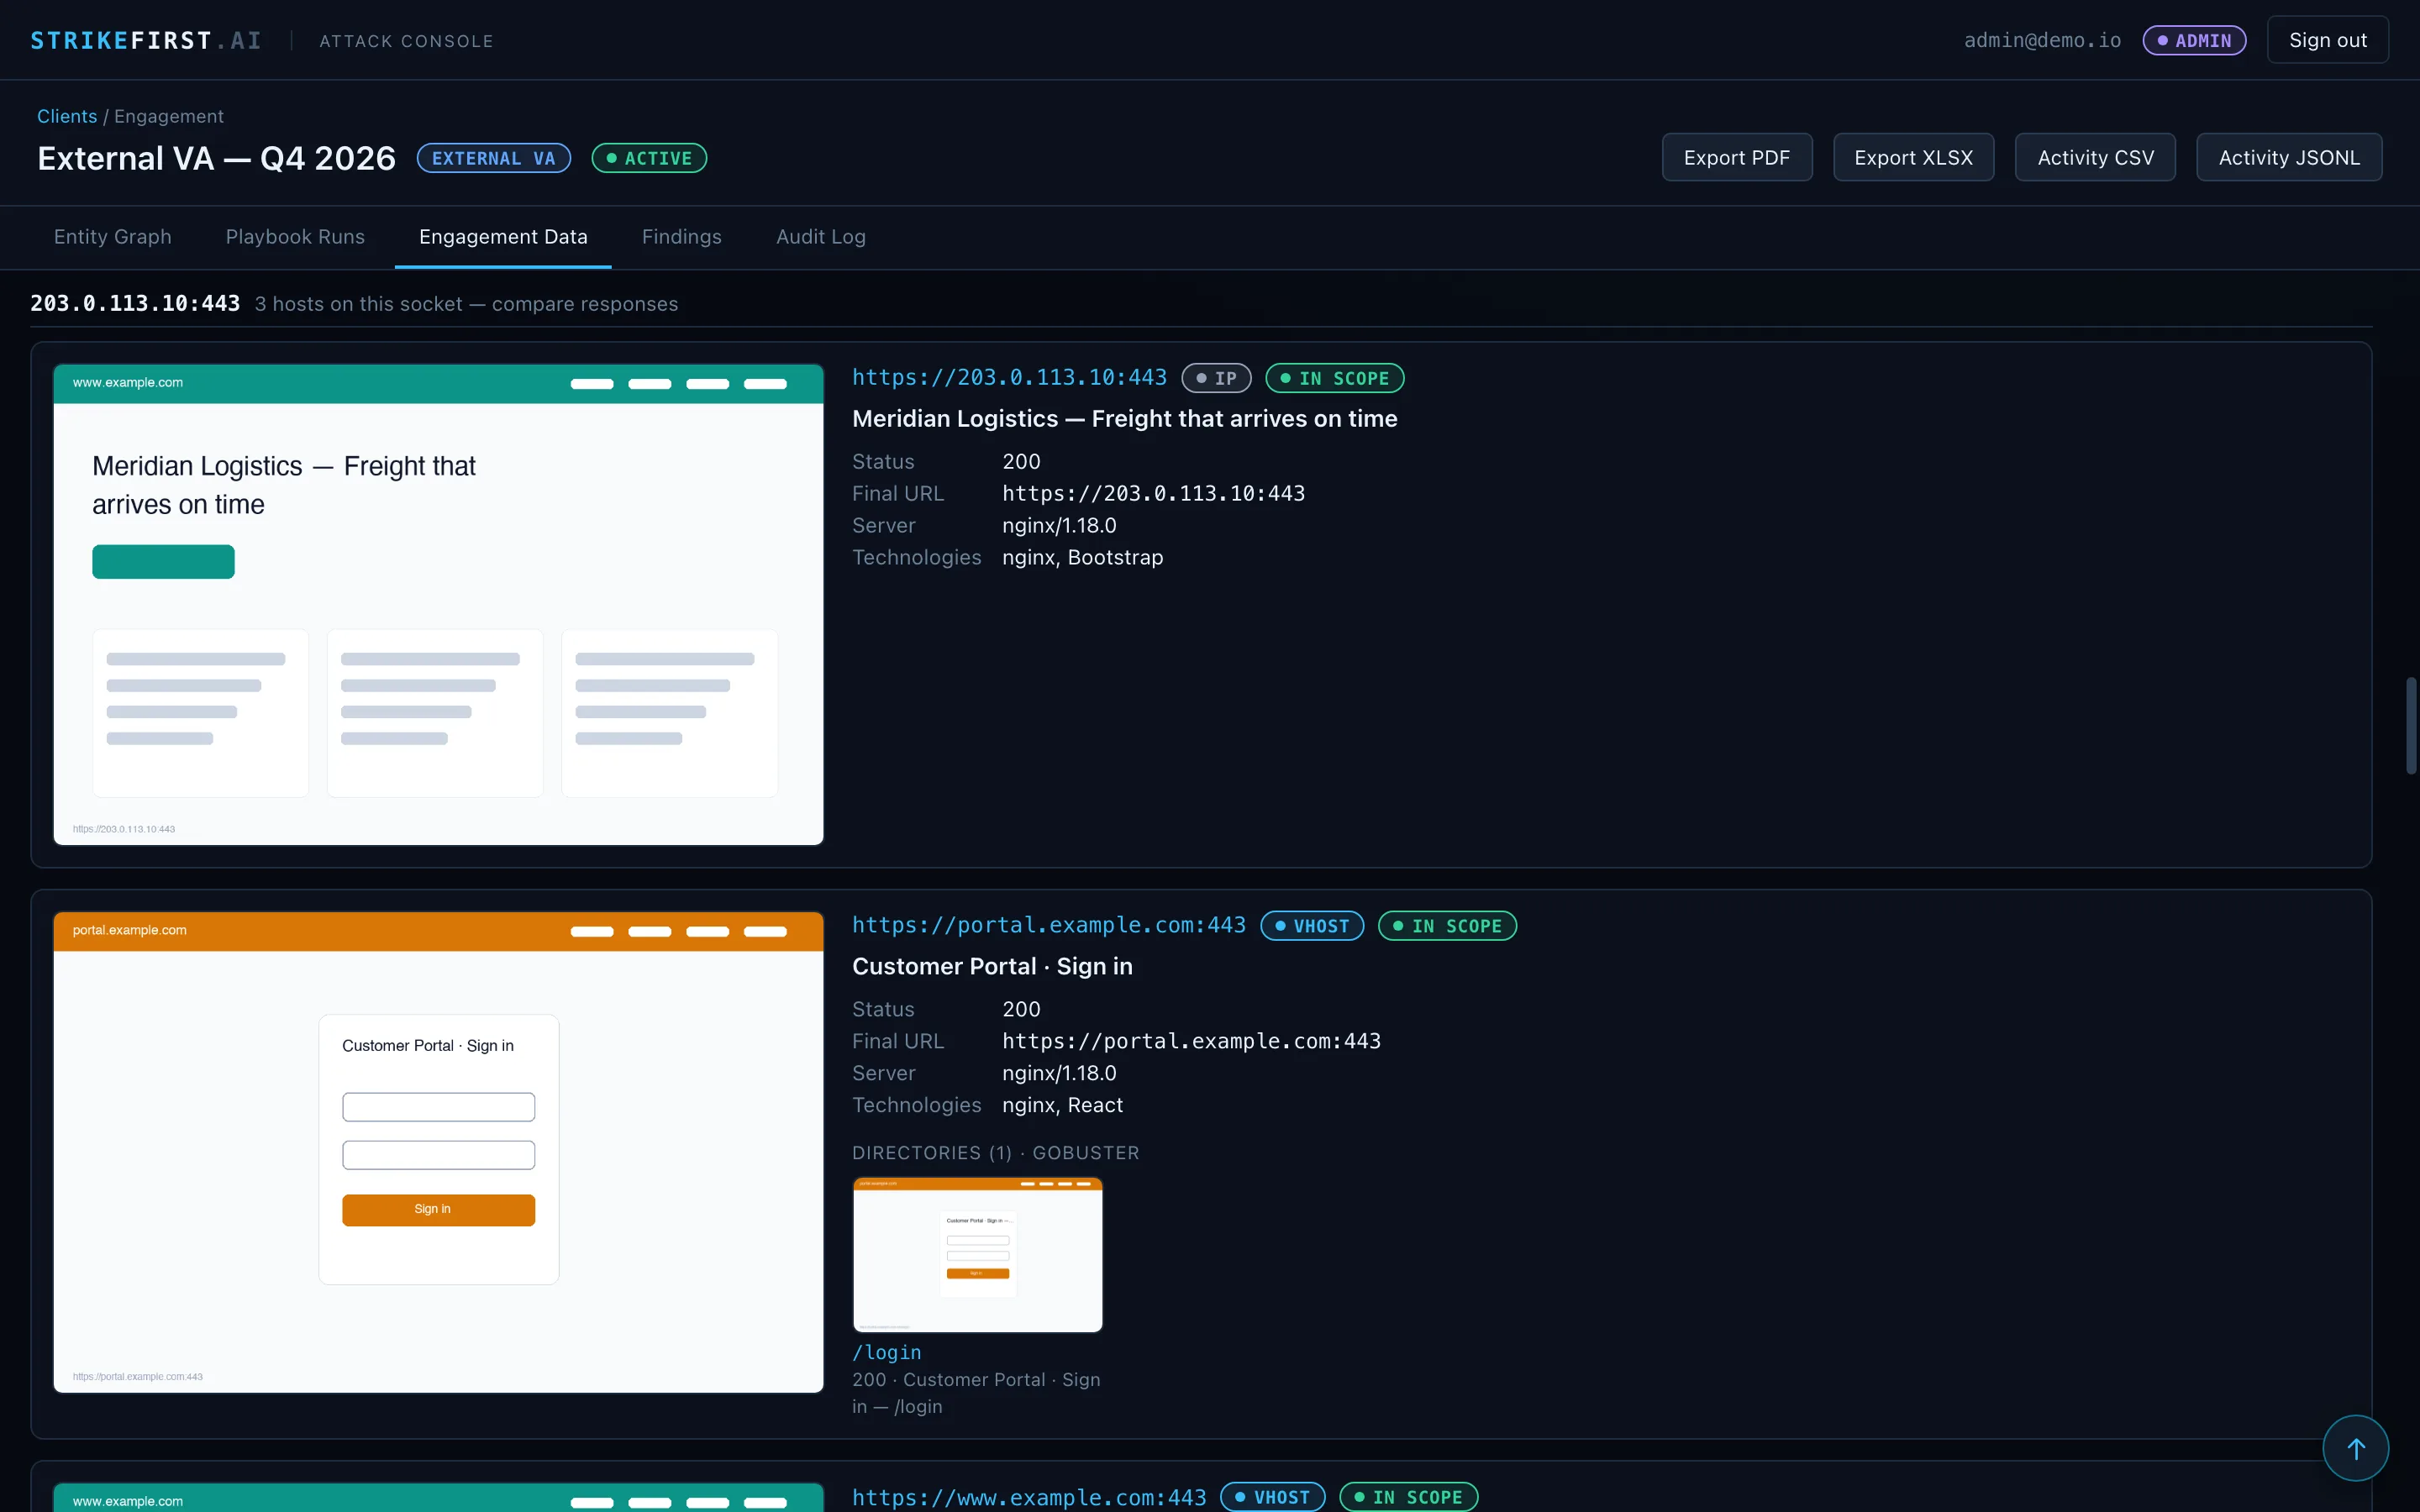
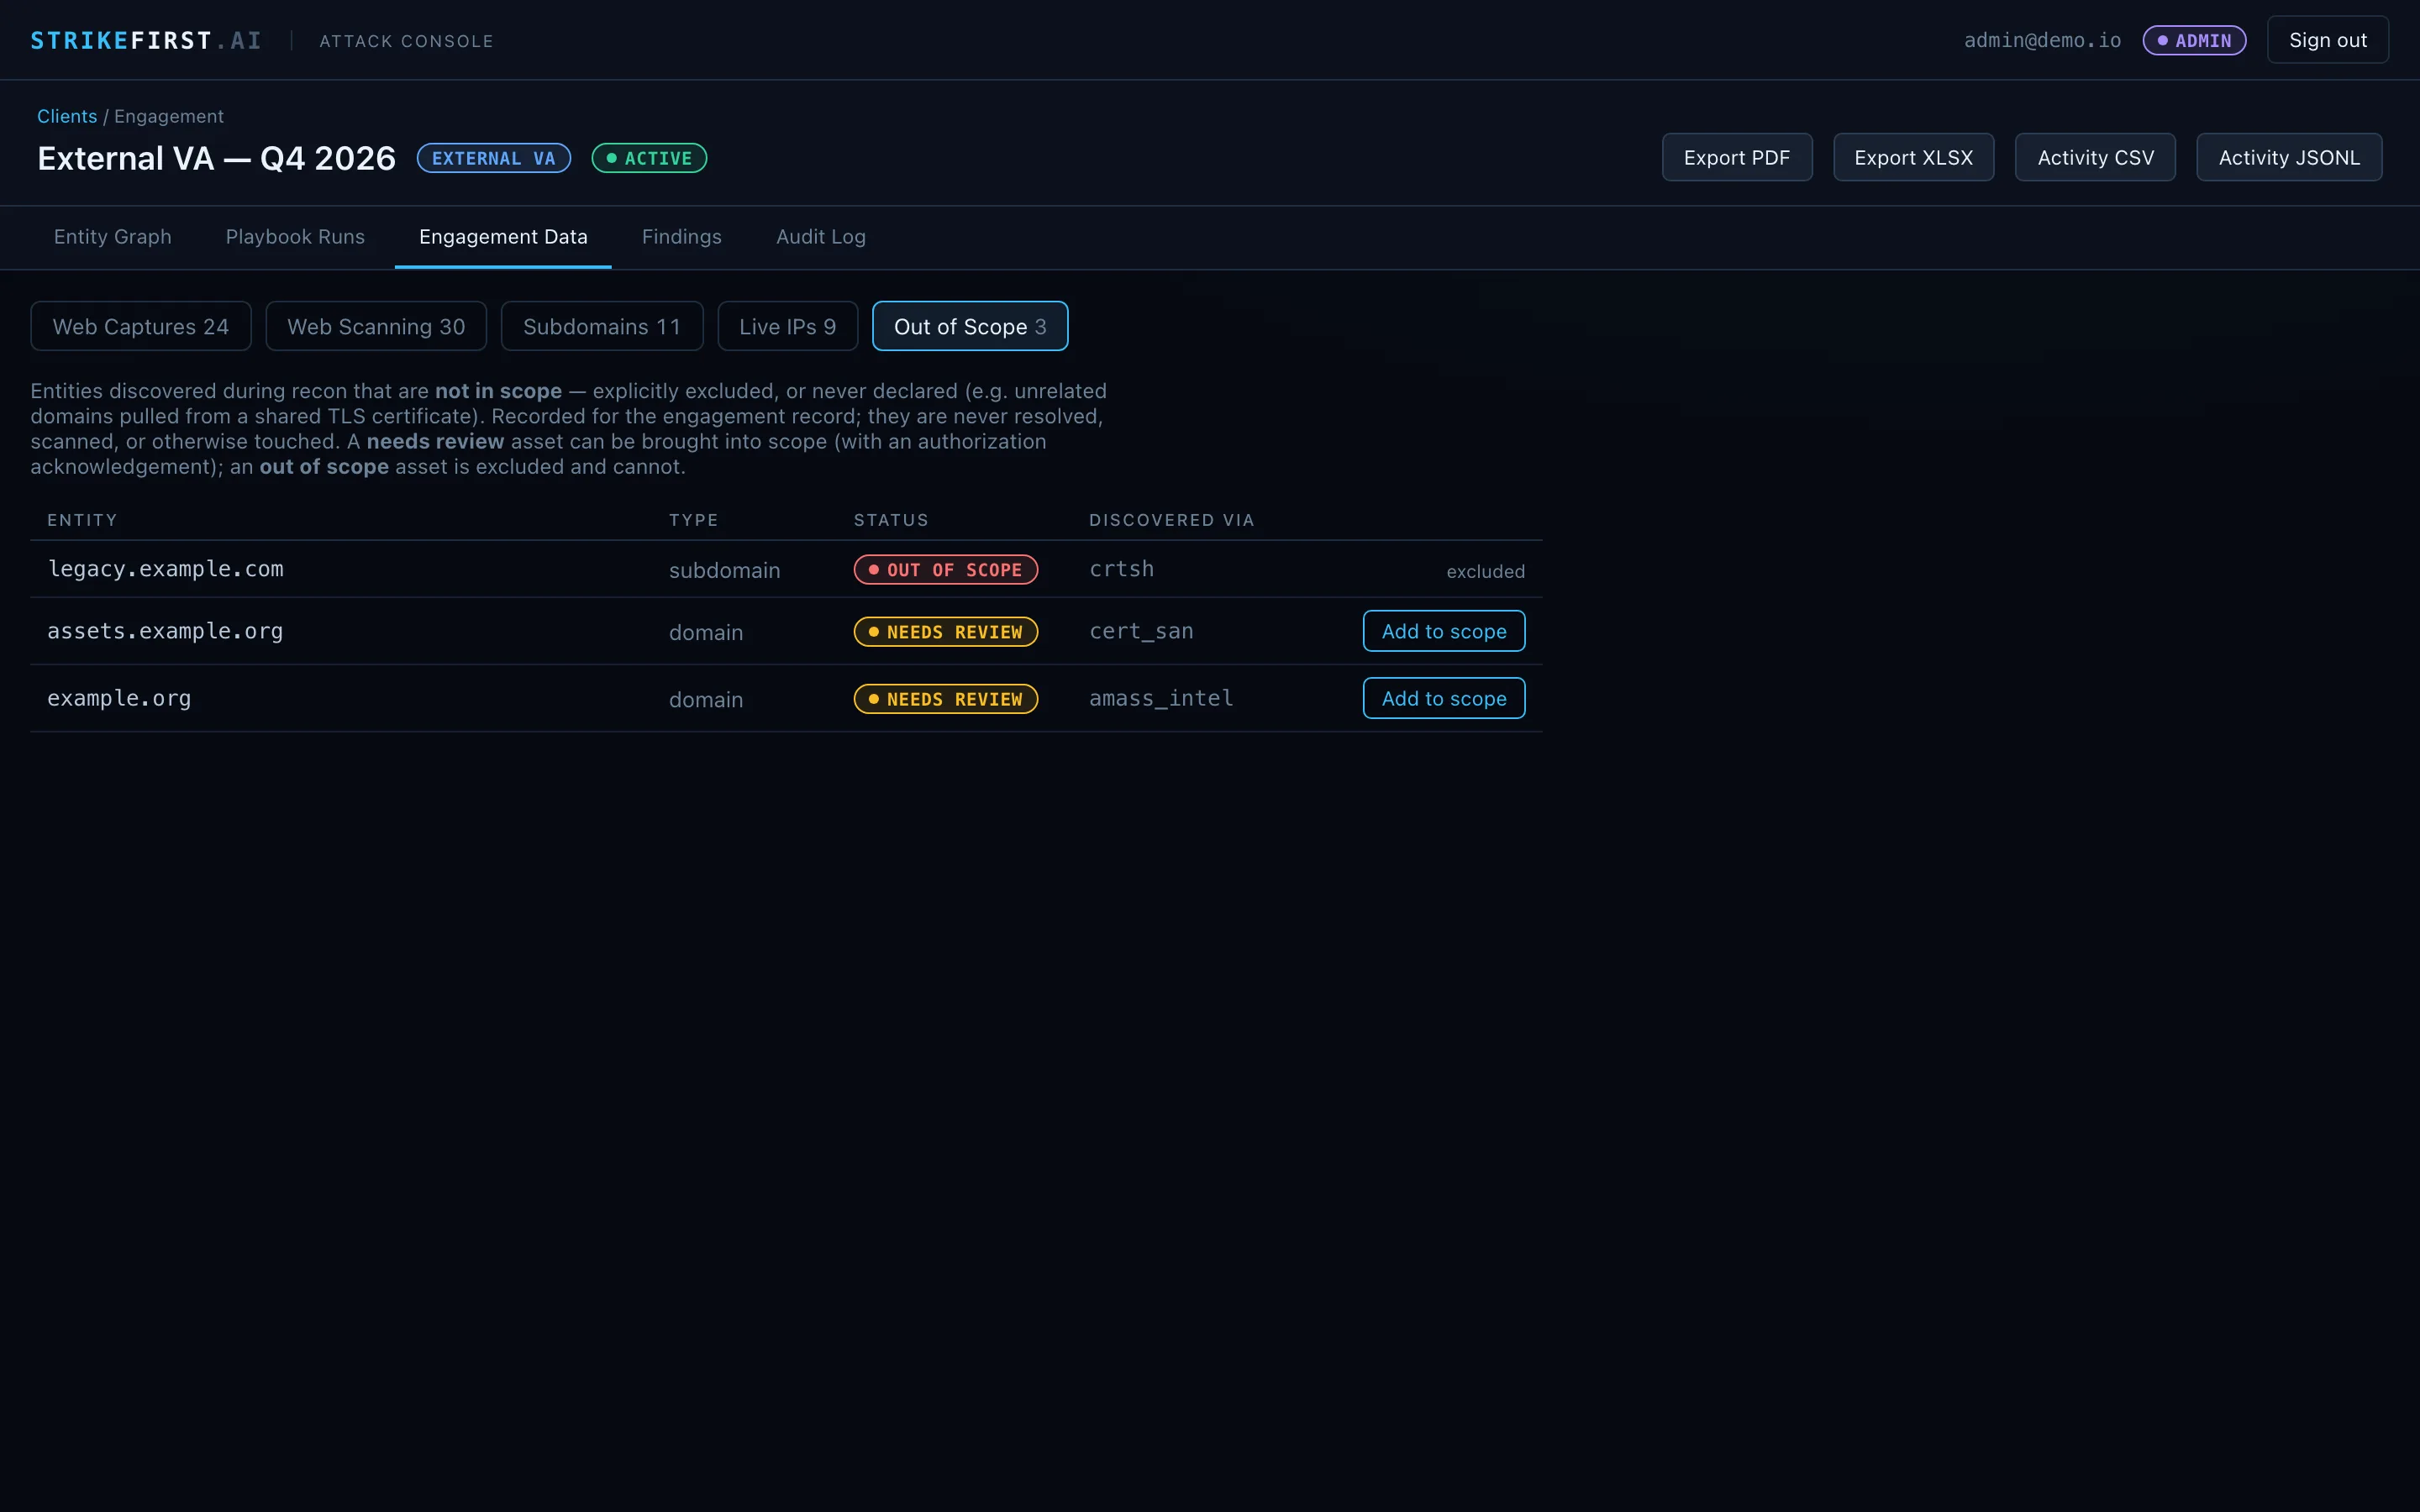
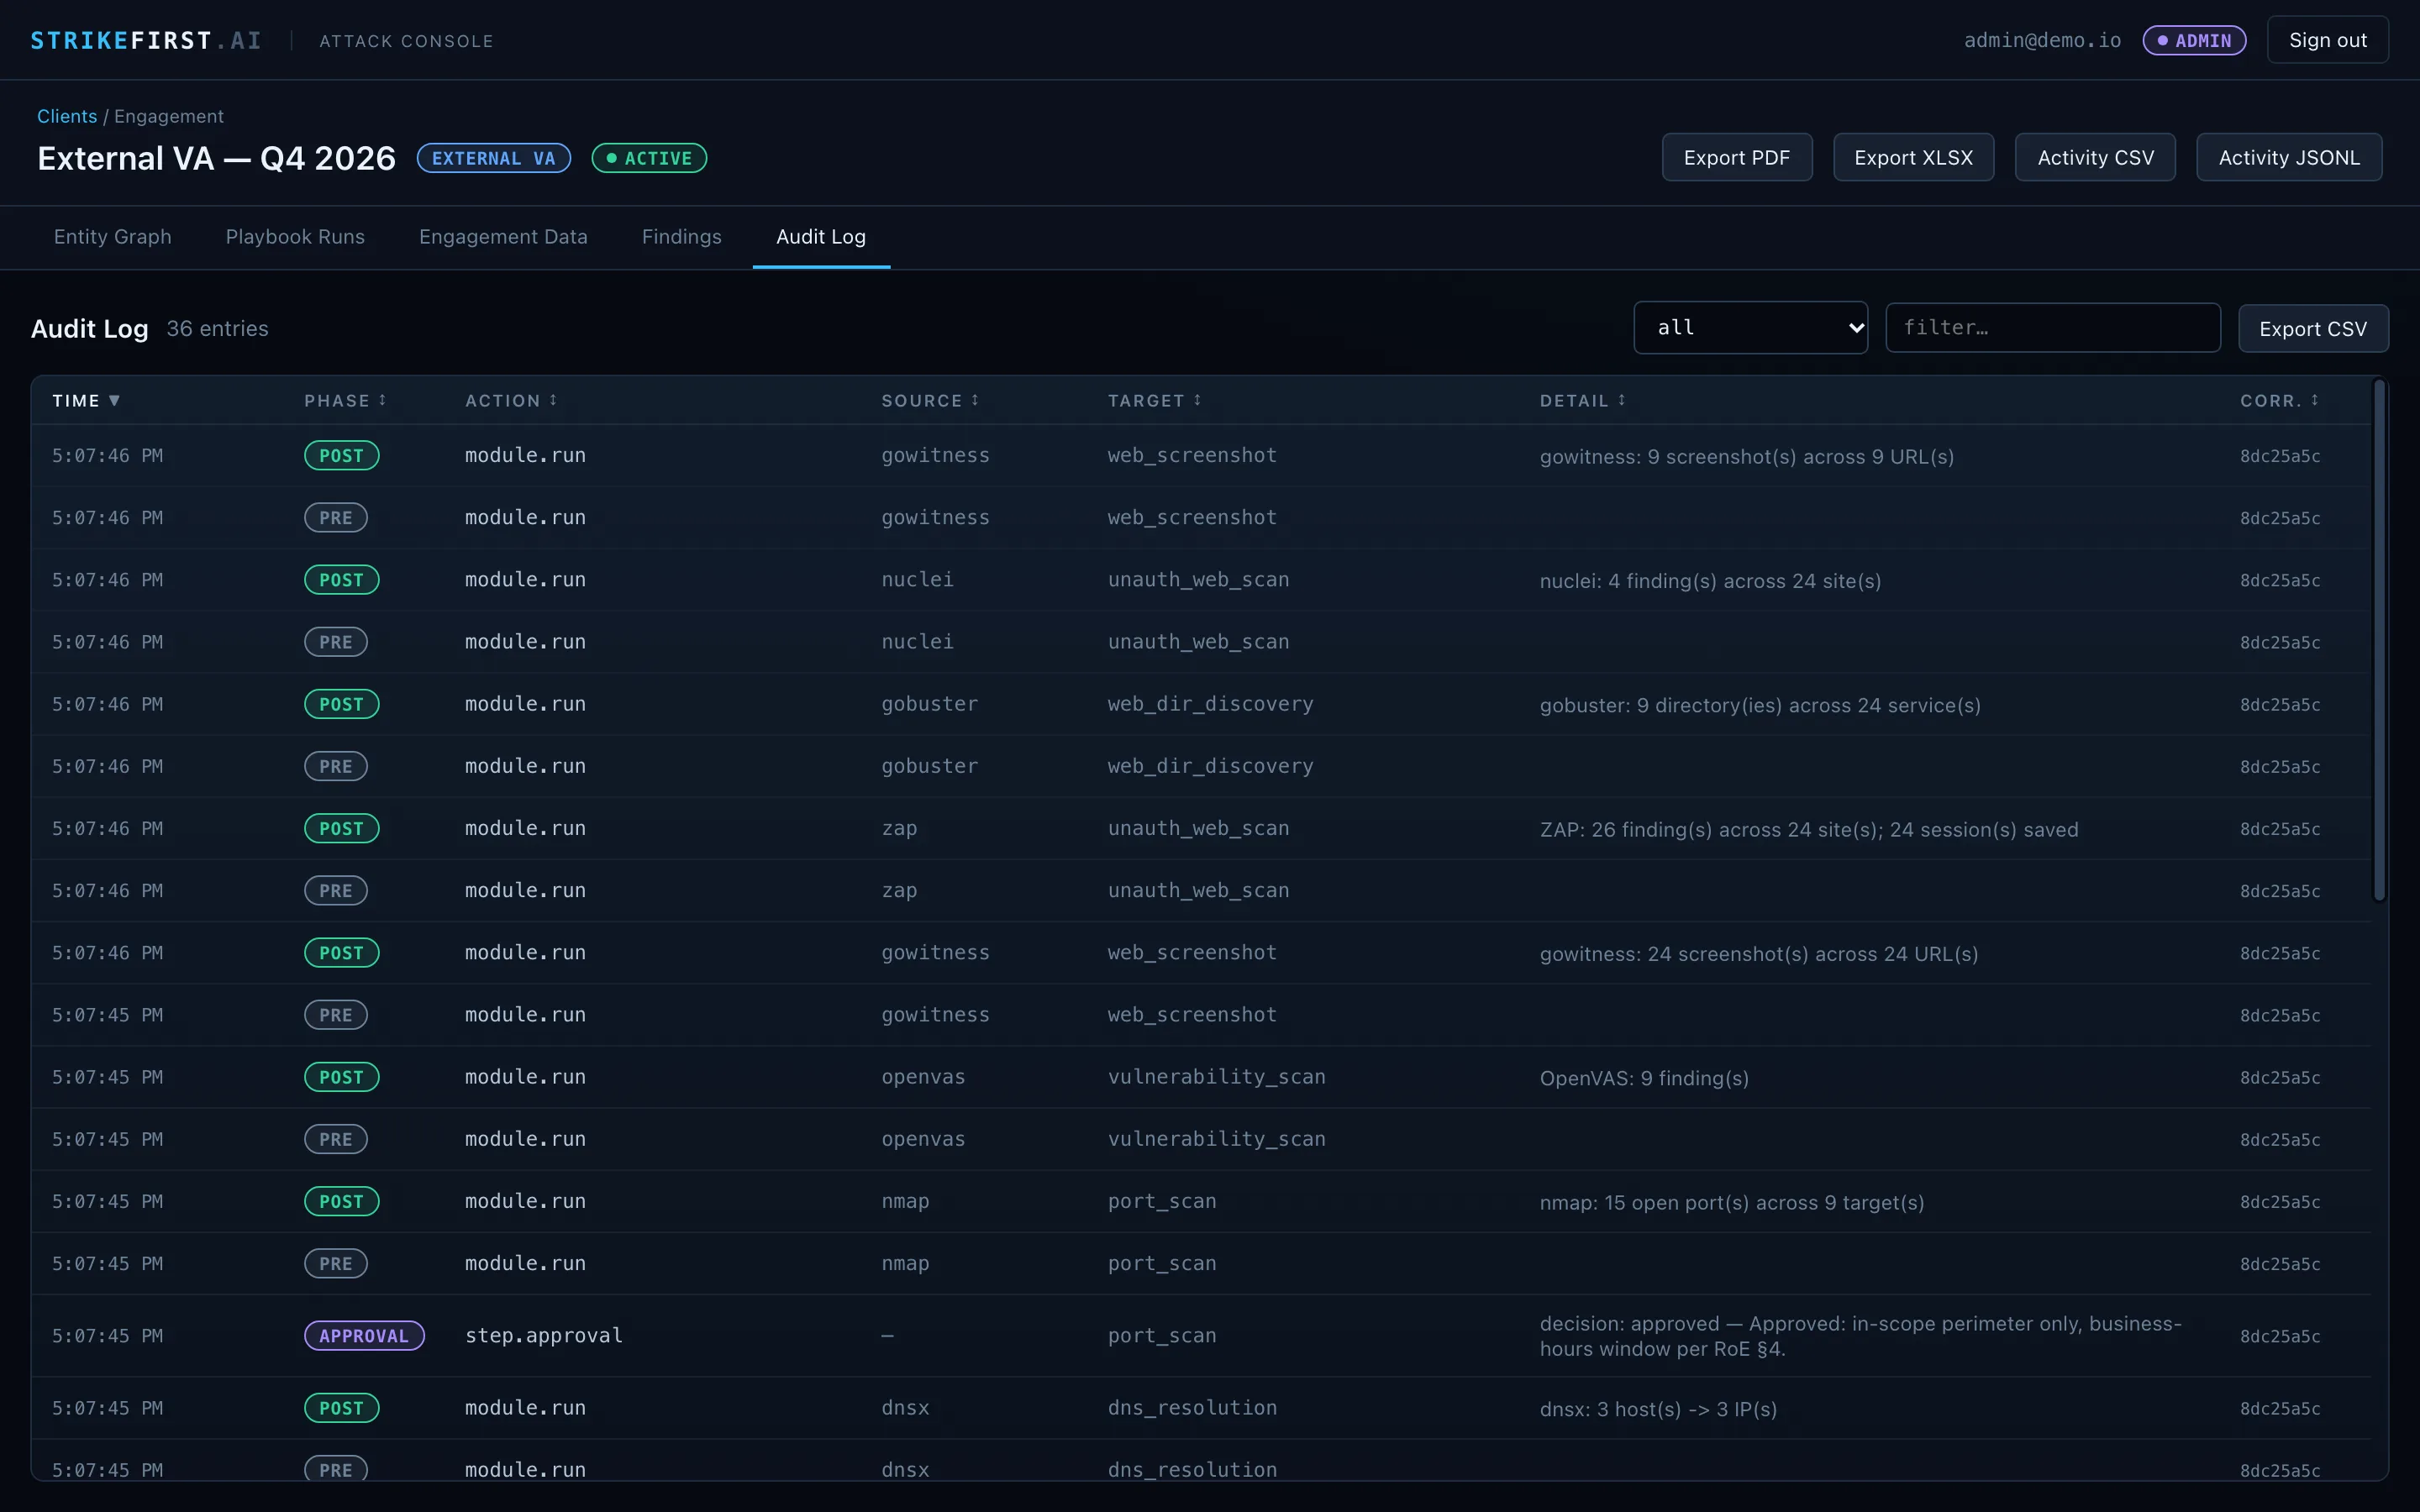
The console, as it runs today.
Real screenshots of the current build, running a fictional engagement against
documentation-only domains and addresses.
strikefirst.net · Attack Console
Trust
Built for authorized work.
The guardrails aren't a policy document. They're how the platform runs.
Scope enforcement
Every discovered asset is classified in scope, needs review or out of scope. Only
in-scope assets feed active steps; the rest are recorded and never touched.
Append-only audit
Pre, post, error and approval entries for every action, correlated per run. The
audit trail outlives the data it describes.
Multi-tenant RBAC
A client-to-project hierarchy with role-based access for admins, leads, operators,
viewers and auditors.
Client-ready reporting
A one-click PDF deliverable with findings by risk, and a multi-sheet XLSX workbook
covering findings, assets, the audit trail and the toolchain.
SOC deconfliction
Hand the client's SOC an activity timeline of every tool execution, with source
addresses and targets, ready to load into the client's SIEM.
Modular by design
Every tool sits behind one capability interface, so new integrations slot in, and
existing ones can be swapped, without rewriting playbooks. Each run records exactly
which tool and version did the work.
Progress
Building in the open.
Where StrikeFirst.AI stands today.
Shipped milestones
Early access
Put your next engagement on rails.
We're onboarding a small group of security teams ahead of the hosted launch:
penetration-testing firms, MSSPs and internal red teams.
StrikeFirst.AI is for authorized security testing only.